Public residential-proxy services appear to have offered routes through internet addresses assigned to the Executive Office of the President, according to security firm Layer3 Intel. The finding behind the White House IP addresses rental reports means a paying customer could make web traffic look as though it came from the White House-associated network. It does not show that anyone reached White House internal systems, identified the device involved, or conducted surveillance.
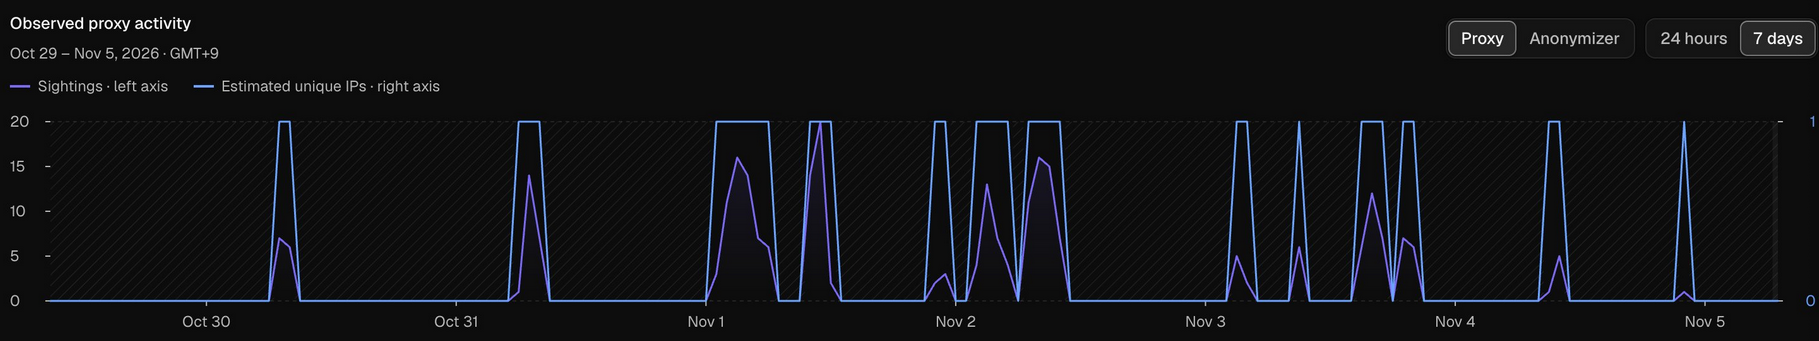
Layer3 Intel said it observed 236 proxy exits through AS2650, the network assigned to the Executive Office of the President, between October 5 and November 3. The firm said the exits involved six IP addresses and appeared on 26 of the 30 days it monitored. It also said 28 residential-proxy services could route traffic through the network.
The company said it did not set out to probe the White House network. Instead, it requested rotating access from public proxy providers and found AS2650 among the routes returned. KrebsOnSecurity reported that the White House did not immediately respond to its request for comment.
What did researchers find on the White House network?
Layer3 reported externally visible proxy exits, not a map of devices or a compromise of the internal network. Its own data, as described by Gizmodo, showed the routes used by proxy customers rather than the person or machine supplying them. The distinction is doing a lot of work here: an IP address can make traffic appear to originate from a network without granting the customer access to other systems on that network.
Most observed activity occurred between 5 p.m. and midnight, Layer3 said. The firm interpreted that pattern as consistent with a person regularly using the network while a device ran proxy software. That is an inference, not an identification of a White House employee, visitor, application, or device.
How does a residential proxy work?
A residential proxy lets a customer send traffic through someone else’s internet connection. To a website receiving that traffic, the request appears to come from the rented IP address rather than the customer’s actual address. Such services can be used for activities including ad verification and testing, but they can also conceal a user’s origin or evade location-based controls.
Proxy nodes can arrive through software-development kits bundled into free apps or browser extensions, according to KrebsOnSecurity and The Verge. Developers may use those kits to monetize installations by selling a slice of a device’s bandwidth. That mechanism explains how a proxy can appear on a sensitive network without establishing why it got there or whether the user knew it was running.
Why did the possible software attribution change?
Synthient initially associated the AS2650 activity with Windows 11 systems running Infatica, a proxy program commonly incorporated into free desktop and mobile software, KrebsOnSecurity reported. Later, Gizmodo reported that Synthient said it had high confidence the likely application was Rave, a shared-streaming app.
Synthient based that later assessment on its observation of Windows 10 and Windows 11 devices communicating with Geonode, Infatica, and Mellowtel, then a VirusTotal search that it said found Rave as the only Windows app containing all three software-development kits. Neither attribution has been independently verified in the available reporting.
Infatica founder Vladimir Fomenko’s hosting company, King Servers, previously hosted six of eight IP addresses used by Russian state security services in attacks on Arizona and Illinois election databases in 2016, KrebsOnSecurity reported. That history does not establish a connection between those attacks and the proxy activity reported on AS2650.
Residential-proxy exposure is a security concern because the services can disguise traffic sources and, in some cases, their software has contained exploitable flaws. But the reported White House proxy exits are evidence of public routing through associated addresses, not evidence that outsiders obtained internal White House access.
This story draws on original reporting from Krebs on Security.